LiteLLM Compromised Again: Infostealer and RAT in 1.107.0
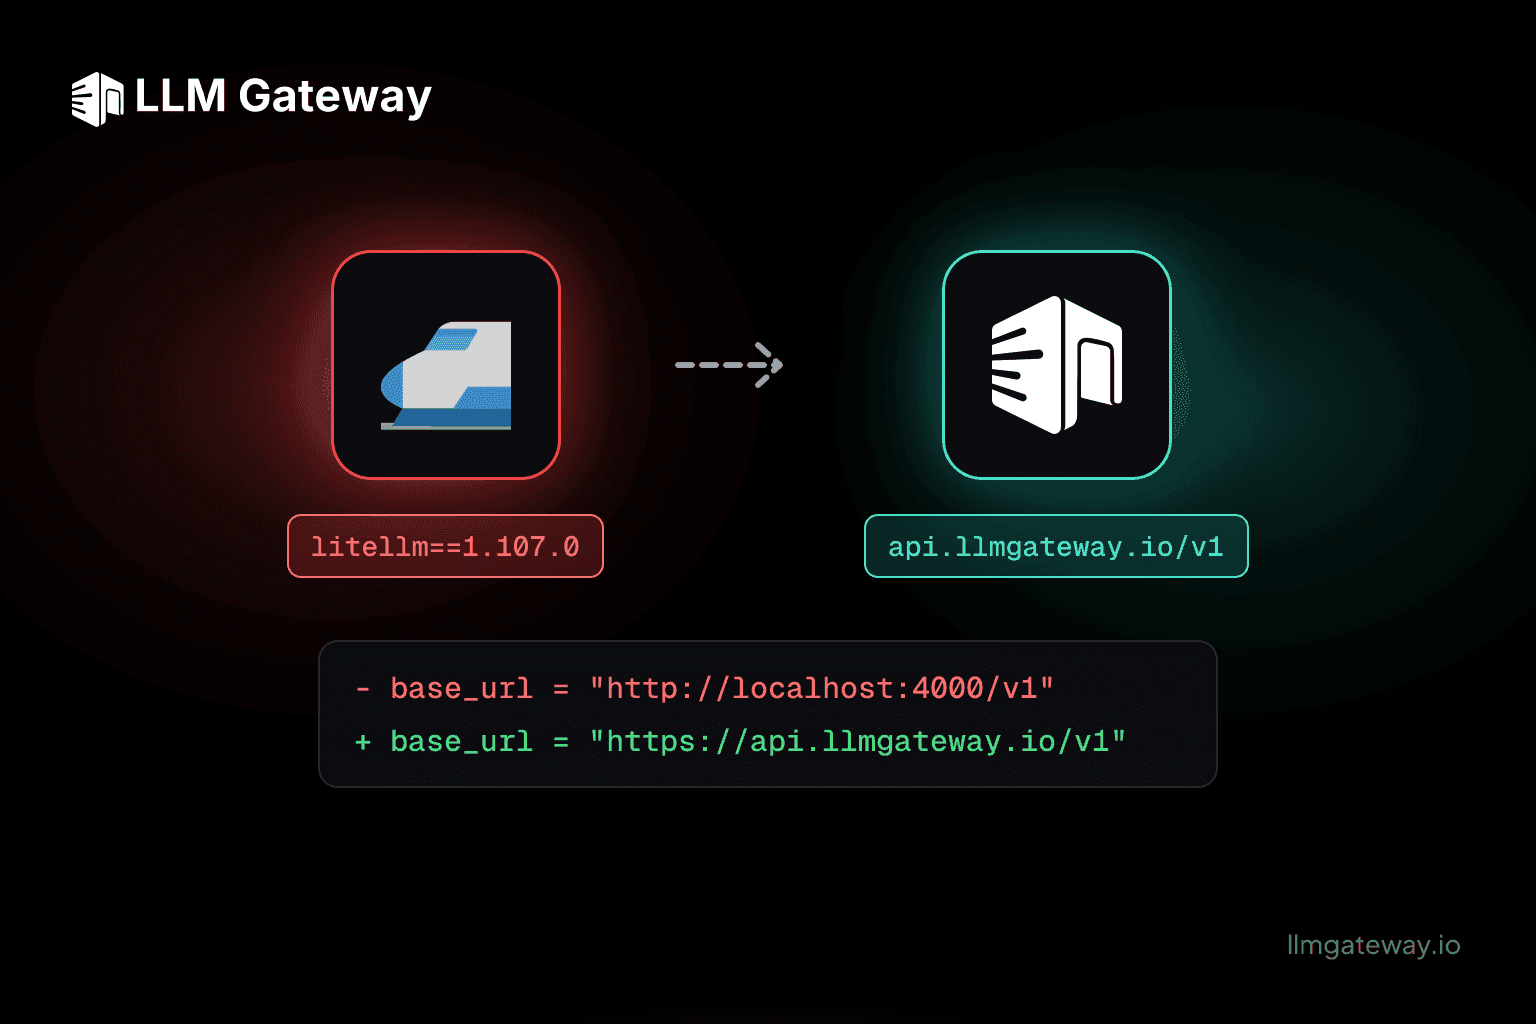
LiteLLM was compromised again on October 21, 2026: version 1.107.0 on PyPI and the official Docker image shipped an infostealer and a remote access trojan that dumped stored provider keys. Here is what happened, how to check if you are affected, what to rotate, and how to move off a self-hosted LiteLLM proxy in two lines.
October 21, 2026